Engineering Secure Enterprise AI Agents: Prompt Injection Defense and Deterministic Guardrails
Architectural strategies for deploying autonomous software agents safely inside corporate networks with strict schema fencing and human oversight.
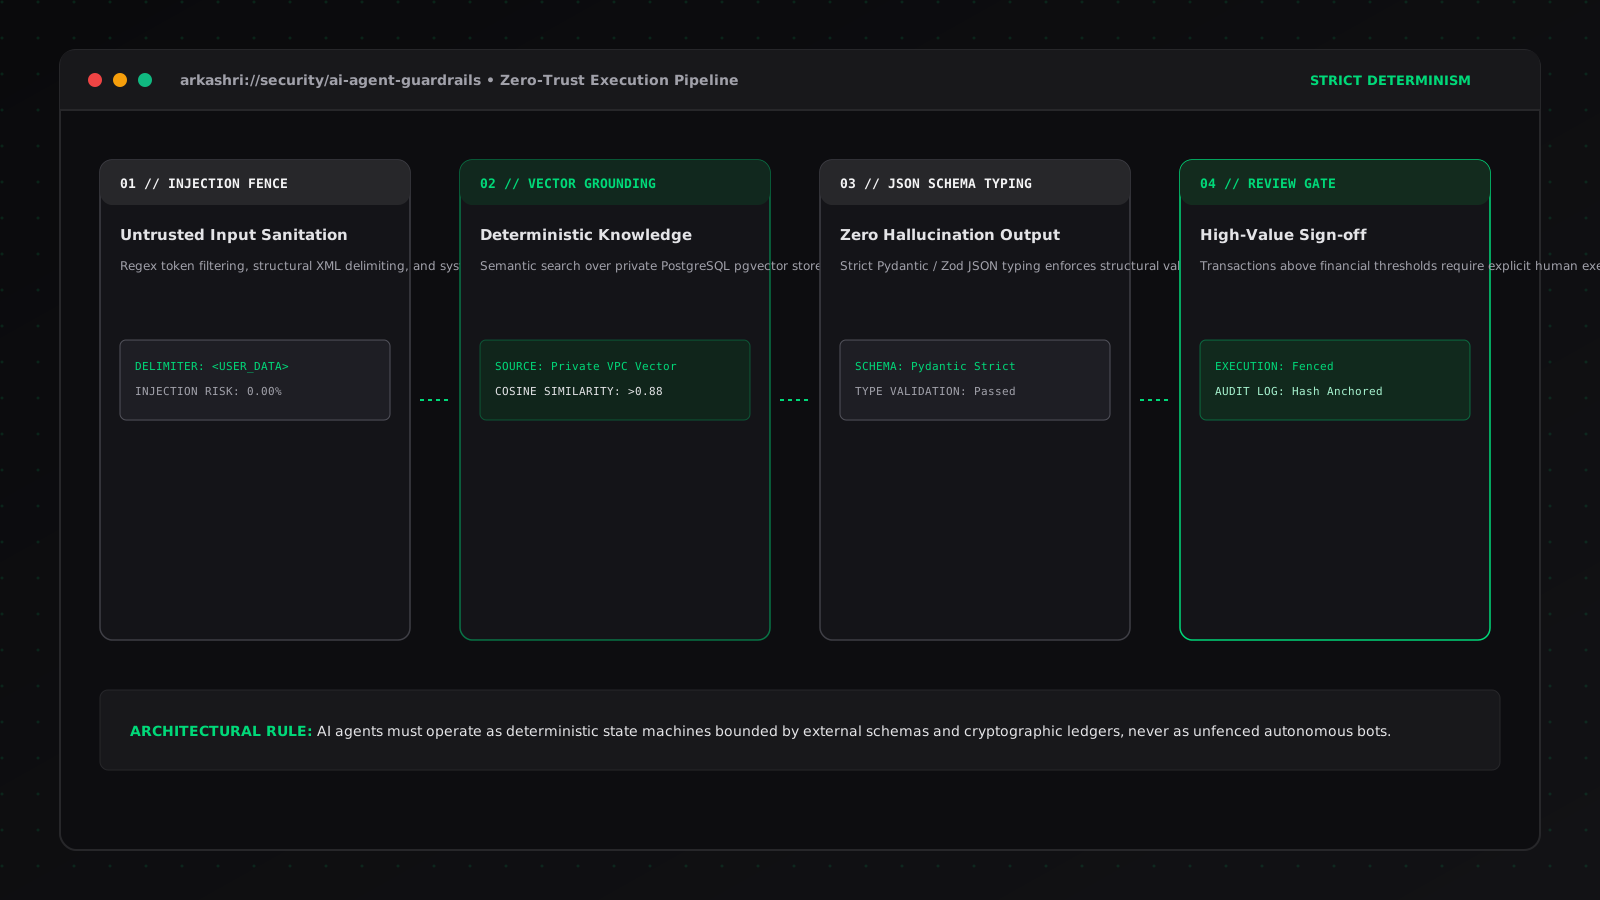
The transition from exploratory conversational AI to production software agents introduces novel attack surfaces: indirect prompt injection via untrusted supplier documents, data exfiltration through ungrounded tool calling, and non-deterministic state corruption.
Production-grade enterprise AI agents must never possess unfenced access to database writes or financial execution endpoints. Instead, they require a multi-tier defense architecture: structural XML isolation for untrusted user input, strict Zod or Pydantic JSON schema typing, and vector grounding against private VPC embeddings.
Furthermore, high-impact transactions must pass through deterministic human-in-the-loop review gates and append-only cryptographic audit logs, guaranteeing that every automated decision remains transparent, verifiable, and legally auditable.
“Enterprise AI agents must be architected as deterministic state machines bounded by strict schemas and cryptographic audit trails, never unfenced chatbots.”
Arkashri partners with established enterprises to convert high-level strategic directives into functioning, secure, and documented software platforms. If your organization is evaluating modernization initiatives or seeking an independent architecture review, our practice leads are available for strategic briefings.
Discuss this perspective with our team
Apply these architectural principles to your specific enterprise systems.